Citrix just removed two 90s-era security standards from the Citrix Workspace app for Mac 2603.10 Tech Preview.
Sessions that worked reliably for years are breaking right now.
Symptom
Session launches, the desktop briefly appears — then the host terminates the connection before you can do anything.
Client logs show:
- ICAEngLoadPd failed: Secure Ica 1.0 is deprecated
- CAPABILITY_SECUREICA2: Host not support Secure ICA 2.0
- PACKET_TERMINATE → Session.Launch.ConnectionFailed
And the VDA confirms it. ICA Service event log:
→ Event ID 3: „You do not have the correct encryption level to access this session.“
The current Public Release still works.
Only the Tech Preview breaks.
The reason is more interesting than the symptom
- DTLS 1.0 has officially been removed from the client
- Secure ICA 1.0 (RC5) is gone as well
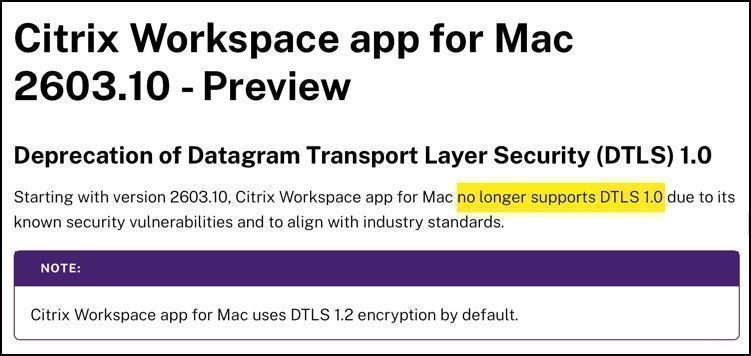
DTLS removal is documented.
Screenshot below — 2603.10 named explicitly, DTLS 1.2 is now the default.
RC5 removal isn’t documented anywhere.
You only see it in the ICA engine log:
→ „ICAEngLoadPd failed: Secure Ica 1.0 is deprecated“
The client can no longer load RC5. If the VDA doesn’t speak Secure HDX yet, the capability negotiation fails — and the host terminates the session with an explicit encryption mismatch.
What this means for CVAD environments
- Mac users on the Preview build are affected today
- Windows Workspace app will likely follow the same path
- Secure ICA has been deprecated server-side since CVAD 2402
- The migration window is shrinking
A note on the Tech Preview status
Specific symptoms may shift between preview builds.
What won’t shift is the direction — RC5 and DTLS 1.0 are leaving the client, the server-side deprecation has been in place since CVAD 2402, and the platform-modernization train has left the station.
The strategic direction is clear: Secure HDX
Application-level end-to-end encryption with AES-256-GCM.
The gateway still routes the traffic — but can no longer inspect it.
From our Secure HDX migrations, one pattern keeps showing up
When you combine Secure HDX with HDX Insight or SmartControl, the gateway needs a new TLS-secured side channel to the VDA — separate from the standard 1494/2598 path.
Firewall rules and certificate chains that were „good enough“ for years suddenly matter on that path.
Audit those before you flip the switch.
Quick self-check
Run this on the VDA during an active session:
ctxsession.exe -v
If the ICA Encryption line still shows RC5 instead of SecureHDX AES-256 GCM —
The move to Secure HDX is overdue. We’re seeing this across multiple @Citrix environments at ceterion. Same direction, different stumbling blocks.
Update 1
Sources, for anyone who wants to verify:
DTLS 1.0 removal — first screenshot is from the official Citrix Workspace app for Mac 2603.10 Preview docs. It’s a rolling EAR page, so the content shifts with each new preview — hence the screenshot rather than a link. Citrix states the Mac client no longer supports DTLS 1.0 and now defaults to DTLS 1.2.
RC5 / Secure ICA 1.0 removal — this one isn’t in any public doc. The evidence comes from a full client-and-server log correlation:
→ engload.m: „ICAEngLoadPd failed: Secure Ica 1.0 is deprecated“
→ wdinit.c: „CAPABILITY_SECUREICA2: Host not support Secure ICA 2.0“
→ session terminates with PACKET_TERMINATE / Session.Launch.ConnectionFailed
→ VDA ICA Service event log (second screenshot), Event ID 3: encryption-level mismatch — confirming server-side that this is exactly the crypto handshake breaking
The same connection succeeds with the Public Release in the identical environment — confirmed by direct comparison. Server-side context: Secure ICA has been deprecated since CVAD 2402.
That asymmetry is the whole point — one change is announced, the other you only find by its effect.
Happy to compare notes if you’re seeing the same in your environment.
Update 2
2603.10 has shipped as a final release (GA, June 4) — it’s no longer a Tech Preview. It’s available as a manual download now; the staged auto-update rollout hasn’t reached devices yet (and may be gated by your GACS/MDM policies), so the exact arrival will vary by environment.
Two entries in the official 2603.10 fixed-issues list are worth highlighting, because they line up exactly with what we saw in the field:
→ „Sessions might disconnect unexpectedly over TCP because of a decryption failure“ (CVADHELP-31790)
→ „Sessions might disconnect unexpectedly after a network interruption“ (CCVADHELP-4930)
The DTLS 1.0 removal is now documented in the stable release notes (not just the rolling preview page): docs.citrix.com/en-us/citrix-workspace-app-for-mac/whats-new
The RC5 / Secure ICA 1.0 side still isn’t called out anywhere in the docs — it remains a log-only finding. The asymmetry holds.
Bottom line: it’s GA. Once it lands in your fleet, anyone still pinning RC5 server-side will feel it — worth planning the Secure HDX move before then.